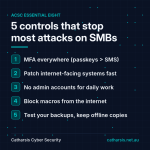
Most breaches at small businesses don’t involve a nation-state attacker or a never-before-seen exploit. They exploit the basics: a...
A penetration test is a planned, authorised attack with rules, a stop button and a report at the end....
A vulnerability scan tells you which known weaknesses might be present. A penetration test tells you which ones an...
Not every data breach has to be reported, but the ones that do have firm rules. This guide explains...
ASD's seventh Annual Cyber Threat Report puts the average self-reported cybercrime cost for a medium business at $141,300, up...
Changing IT providers is mostly about access, documentation and a security baseline. Here is the typical order of work...
A worked example of VLANs for a 25-person Sydney office: the VLAN and subnet plan, which zones may talk...
ISO/IEC 27001 certification follows a fixed path: build an information security management system, run it, audit it yourself, then...
Three frameworks keep turning up in tenders, client questionnaires and insurance forms. They do different jobs: one is a...